An Unprecedented Attack
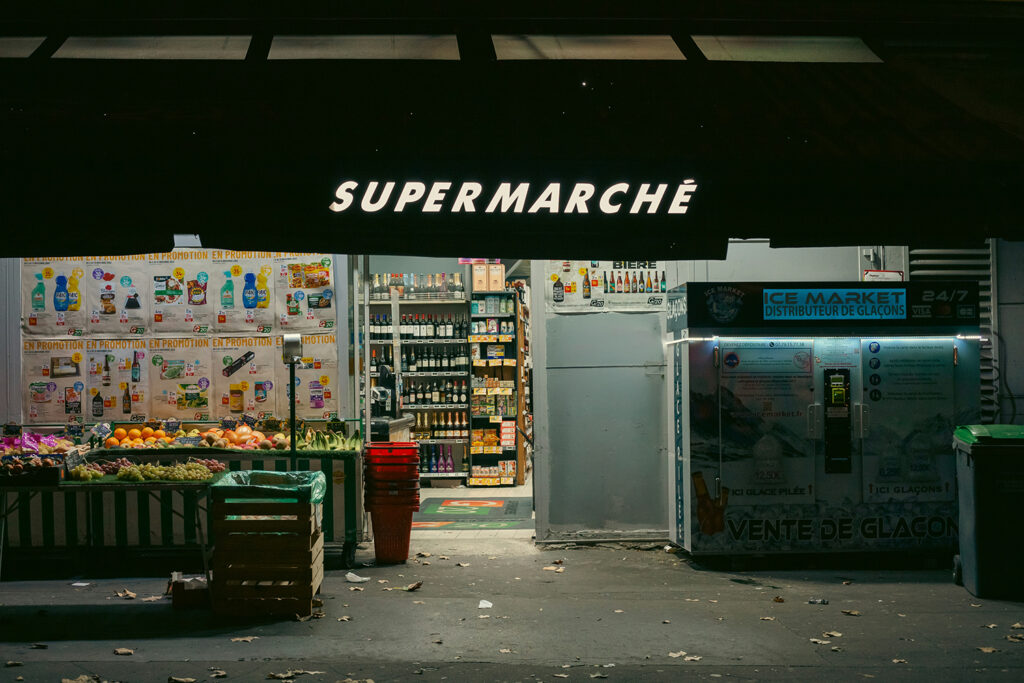
On October 11-12, 2026, hundreds of supermarkets in France experienced an “unprecedented” cyber attack that raised the temperatures of their refrigerators and freezers, which destroyed many millions of euros worth of food, and in some cases caused fires. The attack was perpetrated against an array of companies and may have also affected locations in Spain, Portugal, Poland, Germany, and Belgium.
The Attack Vector
Investigators have not yet verified how the attackers got in. However, on the day of the attack, CERT-FR, a division of France’s national cybersecurity agency, ANSSI, released an alert bulletin which identified “numerous compromises” of Danfoss AK-SM and AK-SC remote controllers for refrigeration systems, as well as Copeland xweb and Dixell xweb models, but had not named the vulnerability or method used in the grocery store attacks.
These systems are typically utilized by store maintenance crews, store administrators, or system owners for remotely accessing cold units via the internet.
Cybersecurity firm Claroty had identified vulnerabilities in the Danfoss AK-SM 800A previous to the attack, and reported that they were able to discover thousands of those control interfaces via the internet in an August 2026 research project. Neither Danfoss nor French authorities have linked Claroty’s findings to this attack.
Danfoss stated that it had provided patches for the AK-SM800A’s identified issues via software updates, but that many of the controllers in the French incident were running outdated firmware, or were models that were no longer supported. They said they had “long advised customers to keep supported systems updated with the latest firmware and to migrate legacy systems to current-generation solutions.”
CERT-FR advised operators to disconnect the devices from the internet or tightly filter internet access.
Remediation
The remediation will likely involve the following steps for impacted devices at every site:
- Remove internet access or limit network access to specific IP addresses
- A full factory reset
- Apply all available security fixes
- Revise authentication credentials
- Update device configuration
Any controller that is outside the manufacturer’s service window will need to be replaced entirely.
A Global Cautionary Tale
This incident should raise serious alarms for companies across the globe as it illustrates the resourcefulness of bad actors and the risks that stem from:
- Internet exposure
- Failing to patch holes created by aging software & hardware
- Retaining software and hardware past its service window
These problems are not uncommon, and the cause is obvious: the cost of upgrades. That is an understandable concern, yet, as demonstrated by the situation in France, the costs of failing to act could be significantly higher than the price of software and hardware upgrades.
Facility managers, owners, and IT professionals should use this crisis as a wakeup call: now is the time to take every available precaution to secure your building automation systems, whether you implement them yourself, or you depend on the Radius Systems team to provide support.
A New Cybersecurity Tool
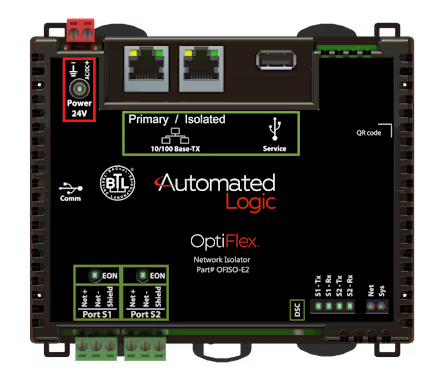
Automated Logic offers a powerful tool which addresses several issues presented by the grocery store attack: the OptiFlex Network Isolator (OFISO-E2). It is designed to isolate BAS networks and act as a firewall for BACnet traffic without routing general IP traffic. This also means that IT staff only need to provide a single IP address for the entire BAS network. The OFISO generates its own downstream addresses for all connected devices.
Cybersecurity Check-up
If you would like to learn more about the OFISO, or you are concerned about the health of your BAS, request a cybersecurity check-up from Radius Systems using the form below. We can:
- Inventory your servers, front-end software, and controllers, identifying anything that is outside its support window
- Review how your BAS network connects to your broader IT environment and identify potential vulnerabilities
- Provide a proposal that will reduce security gaps, addressing the highest risk concerns first and mapping a phased rollout for lower priority items
Below is a cybersecurity checklist to help you begin the review process.
BAS Cybersecurity Checklist
Review the levels of exposure for your facility, software, and hardware. If you’re unable to check three or more of these items, it is probably time for a check-up.
Hardware/Software
- No BAS device is directly reachable via the internet
- Remote access to the BAS processed via VPN or other controlled gateway, rather than port forwarding
- BAS server runs on a supported operating system
- BAS server runs a current, supported version of WebCTRL
- Access to the BAS limited to authorized IP addresses
- BAS network separated from general facility traffic
- Routers act as firewall between customer network and BAS network
- Conduct an external scan of the BAS network to test access by unauthorized users
- Complete firmware and software updates on a regular schedule (when new patches are released)
Credentials
- Forced change of default access credentials on every device
- Logins are unique to each user, no duplication or sharing, with multi-character type requirements and expiration dates
- Closed logins for former employees, contractors, or vendors
- Multi-factor authentication used for any device or software where it is available
- System access is tiered and role-limited
Documentation
- Alarms are set for unusual conditions (such as high temperatures)
- Alarms are communicated to emergency staff after hours
- Document third-party access (contractors, vendors). Close all accounts no longer in use
- A written BAS emergency plan exists and is accessible to applicable facility staff
- Create inventory of what controllers are in use, and what firmware they are running
- Create record of last known functional configuration for controllers
- Inform IT team of the BAS sitemap
- Create replacement plan for equipment approaching end-of-life
- There is clear, documented ownership of system components and processes between facility team and IT team
Redundancy
- BAS databases, programs, and configurations are backed up routinely, offline copies exist outside of the BAS network
- Critical equipment can run safely in manual / fail-safe mode if the BAS goes down
Get a cybersecurity check-up for your building automation system
Sources
- https://www.bbc.com/news/articles/crq5nzxv9q4yo
- https://thehackernews.com/2026/10/attackers-heat-french-supermarket.html
- https://www.reuters.com/business/retail-consumer/french-supermarket-chain-intermarche-hit-by-cyberattack-150-stories-targeted-2026-10-12/
- https://www.abc.net.au/news/2026-10-13/french-supermarkets-hacked-causing-fires-and-food-loss/107258724
- https://cert.cyber.gouv.fr/alerte/CERTFR-2026-ALE-012/
- https://claroty.com/team82/research/freeze-the-controller-defrost-the-food-uncovering-vulnerabilities-in-danfoss-refrigeration-controllers
- https://www.linkedin.com/feed/update/urn:li:activity:7515737848701059072/